Recognise
Bring alerts, observations and client concerns into a defined case.
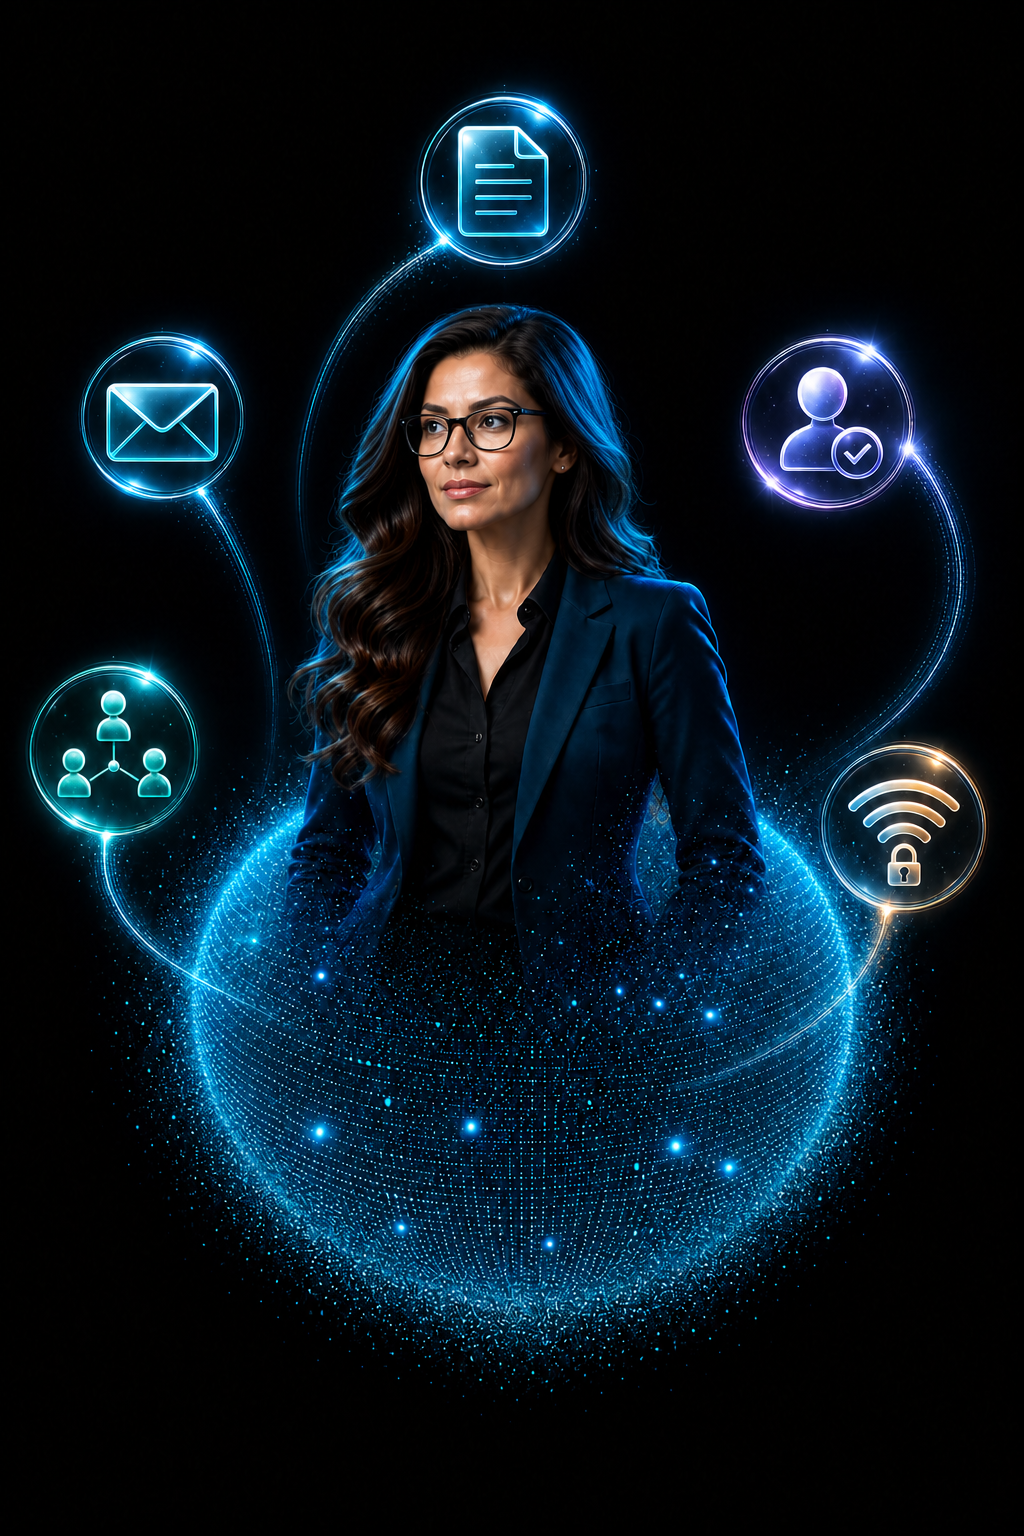
Security investigations rarely begin and end in one product. NetSpectre preserves context as information moves through the full investigation journey.
Bring alerts, observations and client concerns into a defined case.
Retain files, captures, scan results, notes and provenance.
Connect entities, time, context, hypotheses and alternative explanations.
Separate what was observed from what the evidence reasonably supports.
Turn approved findings into clear remediation and client-ready reporting.
Your security tools detect and collect. NetSpectre helps you investigate, validate and turn their evidence into action.
Established cybersecurity technologies are essential. SIEM, EDR/XDR, SOAR, digital forensics and threat-intelligence platforms provide exceptional capabilities for collecting telemetry, detecting threats, examining systems and coordinating response.
The SOCs, MSSPs, MDR providers, DFIR specialists and security teams operating them perform indispensable work. NetSpectre supports that ecosystem by connecting evidence and investigation activity across tools, people and decisions.
Collects and correlates logs across an organisation, enabling security teams to detect patterns and investigate alerts at scale.
Provides rich endpoint or cross-domain telemetry, behavioural detection and powerful response capabilities.
Coordinates tools and automates repeatable security processes so teams can respond faster and more consistently.
Acquires and analyses digital evidence using rigorous methods to understand incidents and preserve technical facts.
Organises indicators, adversary knowledge and campaign context to help teams understand what activity may represent.
Skilled professionals monitor, investigate and respond—often around the clock—using these technologies together.
NetSpectre organises their outputs into a case-centred workspace where evidence can be assessed, validated and developed into traceable findings and clear actions.
Three examples show how specialist platforms retain their strengths while NetSpectre carries selected evidence into the wider investigation.
| Capability | Established strength | How NetSpectre complements it |
|---|---|---|
| SIEM | Centralised telemetry and correlation across large environments. | Carries selected signals into a case-centred evidence, reasoning and reporting workflow. |
| EDR / XDR | Detailed detection, investigation and response across endpoints and connected domains. | Connects endpoint evidence with scans, notes, client context and wider findings. |
| DFIR tools | Deep technical acquisition and forensic analysis of systems and artefacts. | Preserves conclusions, provenance, limitations and client impact within the wider picture. |
Three specialist systems with distinct responsibilities, connected by evidence, scope and meaningful human control.
 Cyber Investigation Intelligence
The central workspace for turning mixed cyber evidence into traceable findings, quality-gated reports and clear client actions.
 Defensive AI & System Protection
The defensive layer designed to recognise suspicious change and support controlled, evidence-preserving response.
 Authorised Vulnerability Discovery
The validation layer for discovering and assessing weaknesses inside an explicitly authorised security scope.
Vale is the evidence-bound intelligence layer being developed across the NetSpectre ecosystem. Her role is to correlate, explain and recommend—not to replace professional judgement or invent certainty where the evidence does not support it.
Recommendations remain connected to the records that support them.
Impactful actions require explicit authority and controlled scope.
Competing explanations and uncertainty remain visible.
The investigator retains authority over decisions and delivery.
NetSpectre is built around authorised work, preserved evidence and honest claims. It supports investigators without overstating what technology—or AI—can prove.
NetSpectre is being developed as a privacy-conscious investigation workspace for organisations, cyber professionals, education partners and carefully scoped pilot engagements.
A cyber investigation brings together digital evidence to understand what happened, what remains uncertain and what action is supported. Explore how scope, evidence preservation, analysis and human review fit together.